
DPO Insights
Authoritative guidance for Data Protection Officers navigating DPDPA 2023. Strategic frameworks, operational blueprints and governance principles written by practitioners for practitioners.
 Legislative Analysis
Why DPDPA Is A Techno Legal Enactment
The DPDPA 2023 fundamentally differs from conventional legislation. It does not simply prescribe obligations and penalties. Instead it creates an architecture where legal compliance is impossible without technological infrastructure. This is not accidental. The drafters understood that data protection in the digital age cannot be achieved through paperwork alone.
 DPO Operations
What Every DPO Should See On Their Dashboard Each Morning
Every DPO faces the same challenge. Section 10 creates accountability for compliance oversight. But oversight requires information. Without structured daily monitoring the DPO operates on assumptions and periodic reviews. This approach fails when incidents occur between reviews or when gradual drift creates compliance gaps.
 DPO Strategy
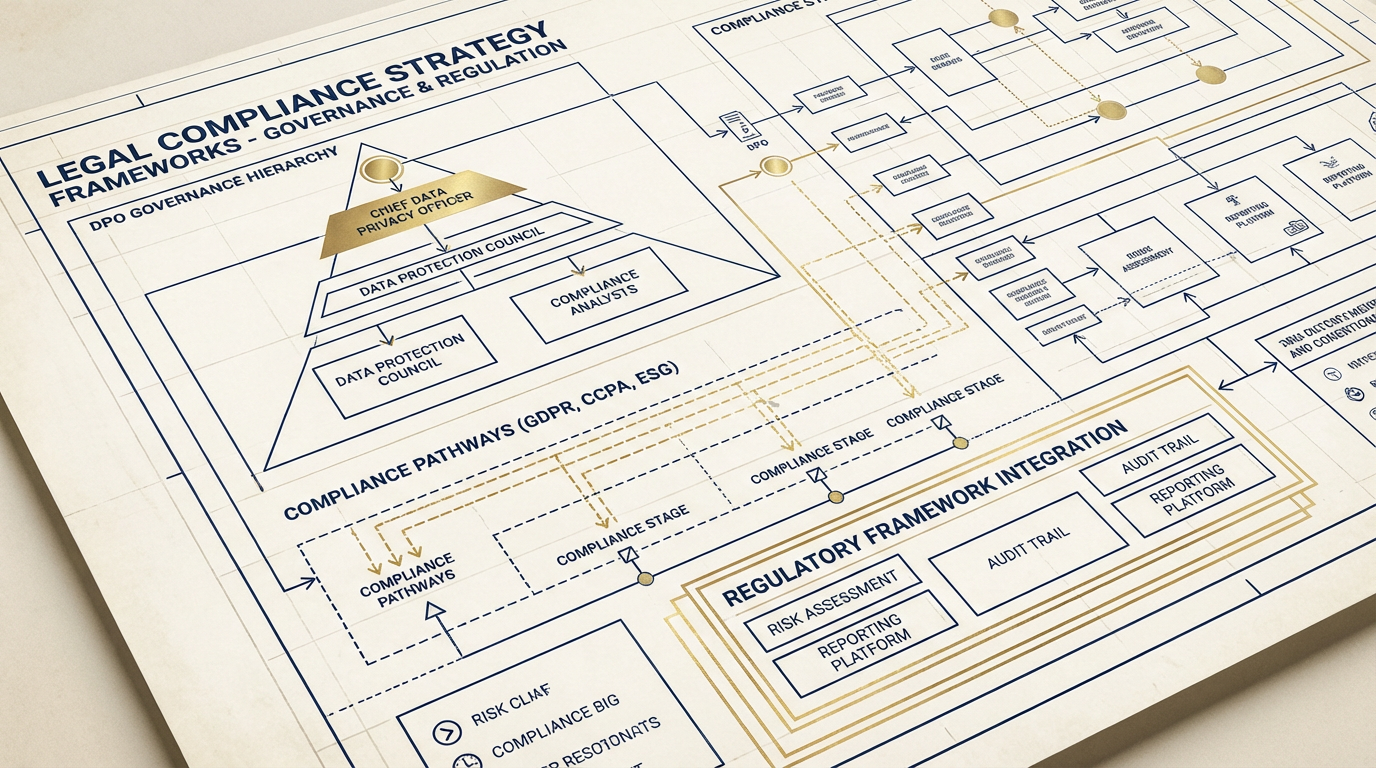
Building Your DPO Strategy: A Practitioner Blueprint
Most DPO appointments begin with enthusiasm and end with frustration. The role demands strategic thinking but organisational structures rarely support it. This blueprint provides the framework that transforms the DPO function from reactive compliance firefighting to strategic risk management.
 DPO Appointment
When To Appoint A DPO: Timing and Triggers Under DPDPA
Section 10 mandates DPO appointment for Significant Data Fiduciaries. But this statutory trigger is the minimum. Sophisticated organisations appoint DPOs before mandatory thresholds because the function delivers value beyond regulatory compliance.
 DPO Governance
Why Your DPO Needs Board Level Access
Section 10 requires the DPO to represent the organisation before the Data Protection Board. This regulatory interface demands board level credibility. But the case for board access extends beyond regulatory representation to effective governance.
 DPO Operations
How A DPO Should Navigate The First 90 Days
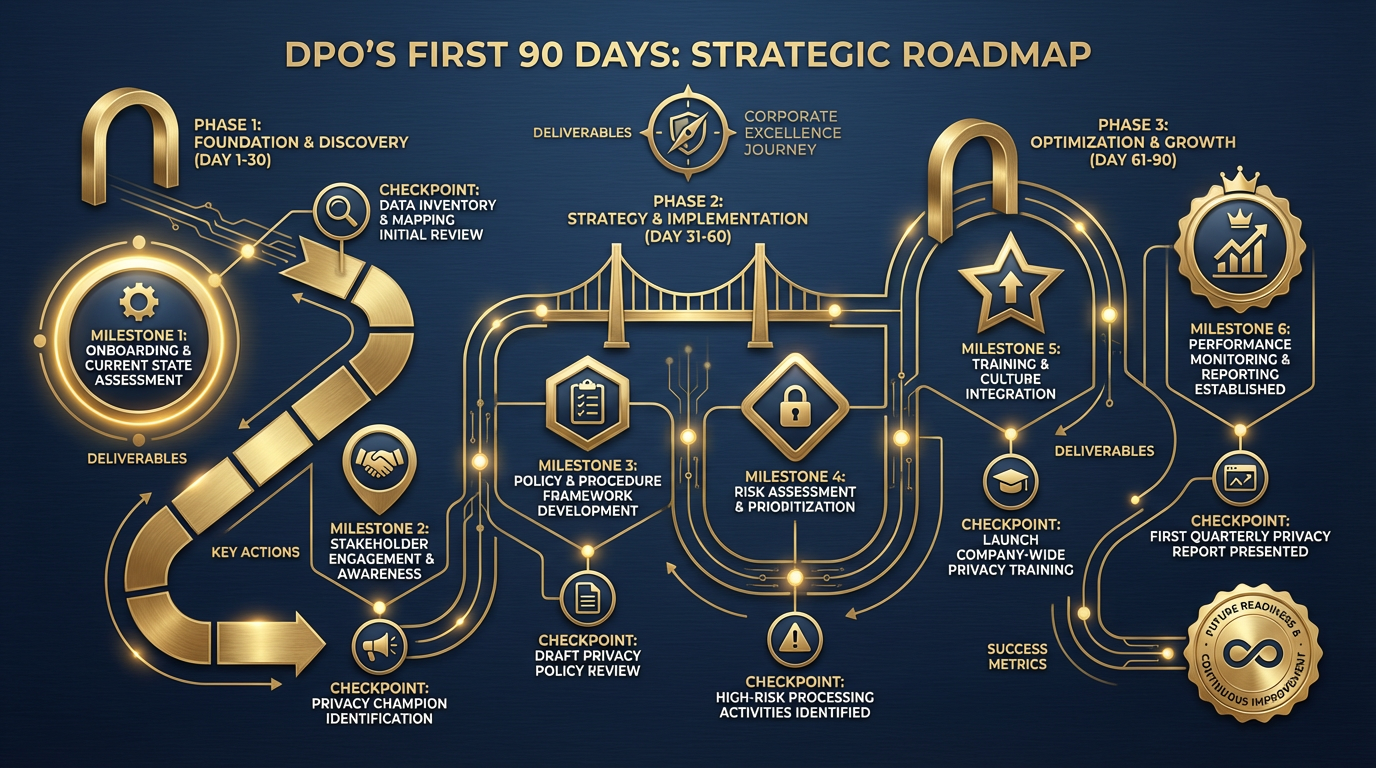
New DPO appointments fail most often in the first 90 days. The DPO either establishes credibility and operational foundation or becomes marginalised. This structured approach ensures the foundation supports lasting success.
 DPO Planning
The DPO Compliance Calendar: Critical Deadlines You Cannot Miss
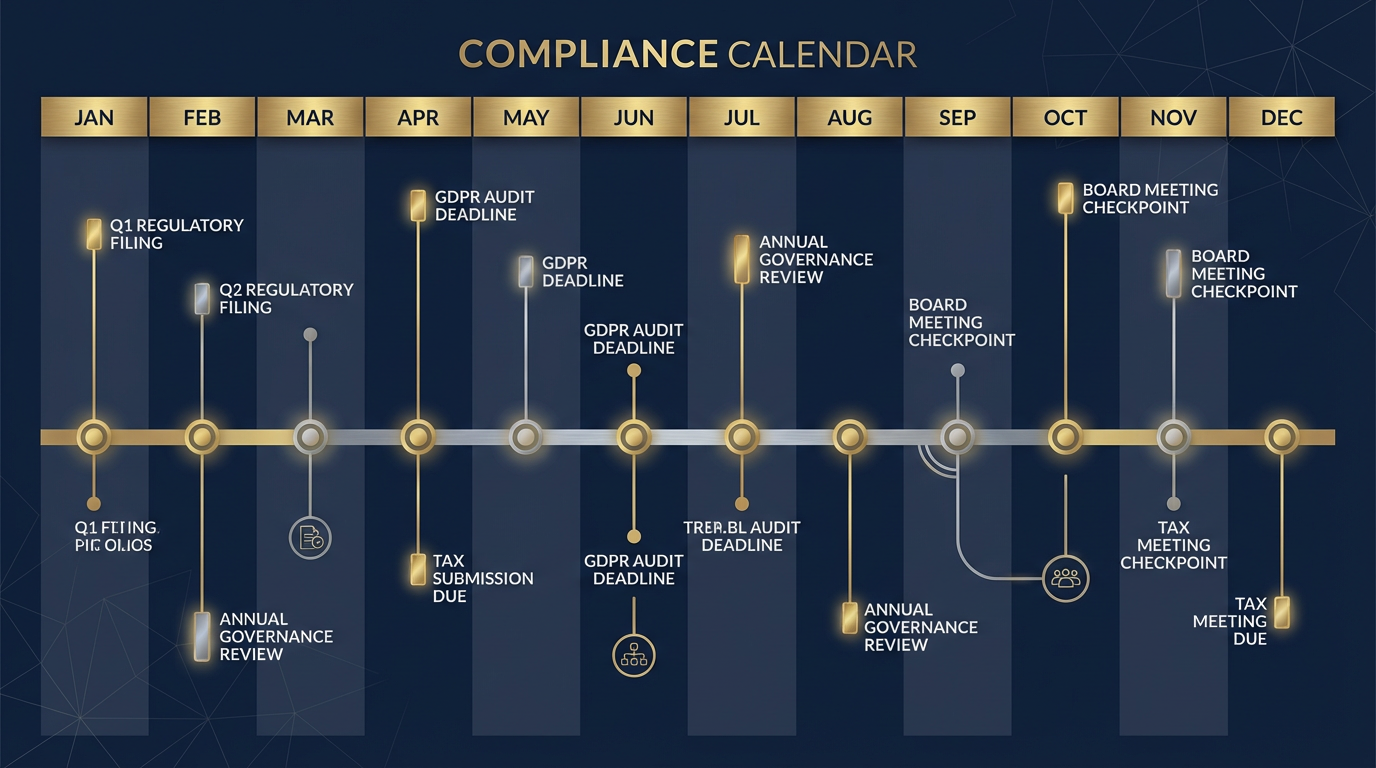
DPDPA creates multiple compliance obligations with defined timelines. Some are event triggered like breach notification. Others are periodic like annual audits. The effective DPO maintains a compliance calendar ensuring no deadline is missed.
 DPO Governance
Why DPO Independence Is Non Negotiable
The DPO role contains inherent tension. The DPO is employed by the organisation but must sometimes oppose organisational decisions. Without structural independence this tension resolves in favour of the employer every time. The regulations recognise this and create independence requirements.
 Rights Management
How DPOs Should Handle Data Subject Rights Requests
Sections 11 through 14 create rights that data principals can exercise against your organisation. These rights become operational reality when requests arrive. The DPO must ensure the organisation can receive, process and respond to rights requests within statutory timelines.
 Audit and Assurance
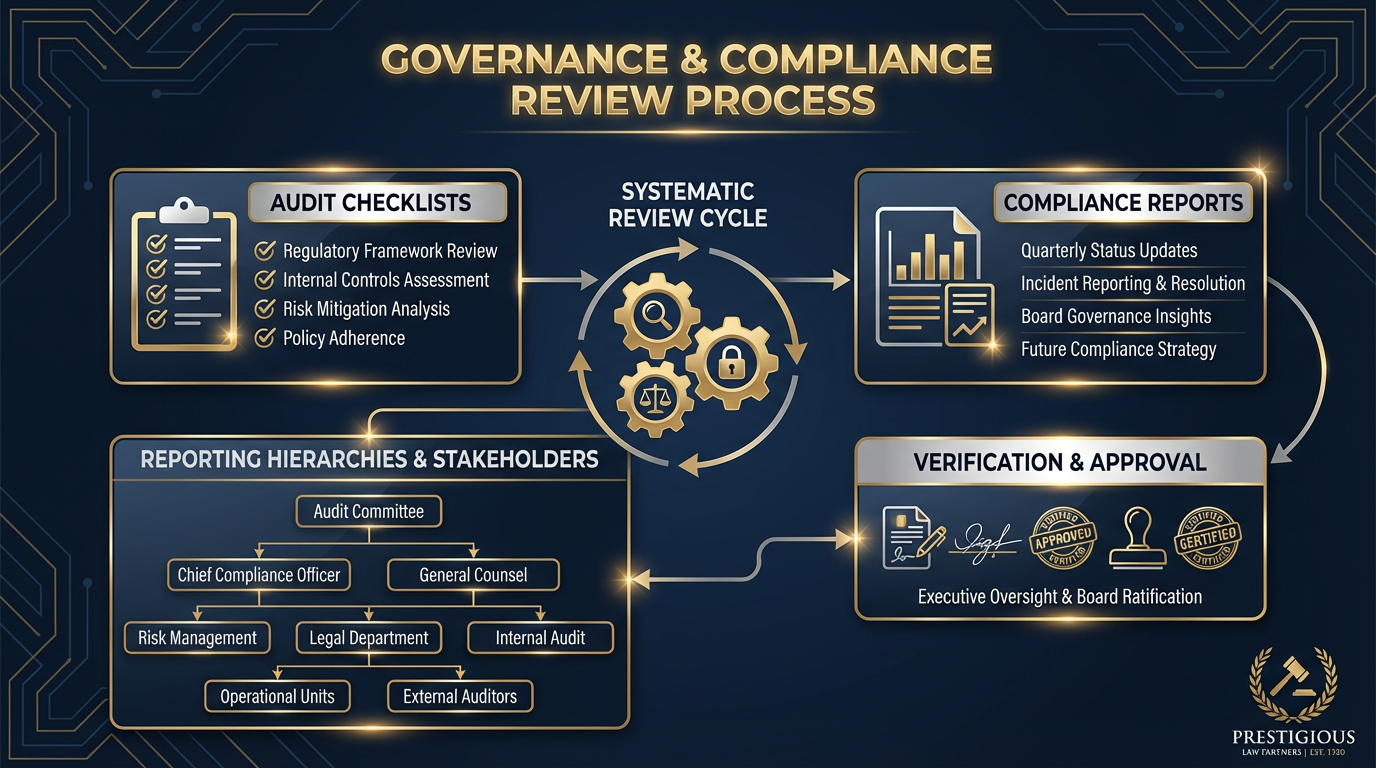
The DPO Audit Function: What Every Board Member Should Know
Section 10(2) requires Significant Data Fiduciaries to conduct annual audits of DPDPA compliance. Board members often misunderstand this requirement. It is not internal review documented for file. It is independent assessment submitted to the Data Protection Board.
Frequently Asked Questions About DPO Under DPDPA
When is DPO appointment mandatory under DPDPA?
DPO appointment is mandatory for Significant Data Fiduciaries under Section 10(2) of DPDPA 2023. The Central Government determines SDF classification based on volume and sensitivity of data processed, risk to data principals, and use of emerging technologies.
What are the key responsibilities of a DPO under DPDPA?
Under DPDPA, DPO responsibilities include serving as point of contact for data principals, representing the organisation before the Data Protection Board, overseeing compliance activities, conducting or coordinating annual audits for SDFs, and advising on data protection impact assessments.
Must the DPO be based in India?
Yes, Section 10(2) explicitly requires the DPO to be based in India. This is a statutory requirement for Significant Data Fiduciaries and cannot be fulfilled by appointing a foreign based officer.
What is the annual audit requirement for DPOs?
Section 10(2)(d) mandates annual compliance audits by independent Data Auditors for Significant Data Fiduciaries. Audit reports are submitted to the Data Protection Board and serve as regulatory evidence of compliance pulse.
Need DPO Advisory Services?
Our team provides strategic DPO advisory, compliance framework development and regulatory representation services.
Get in Touch